 Goran Štimac
KubeVirt and the VM-Container Convergence
KubeVirt ships Beta feature gates on by default, cross-architecture VMs, CBT backups, confidential computing, and AI/GPU placement — one control plane for VMs and pods.
Tag
11 matching blog articles with repeat coverage under this topic.
Tag wiki
Definition
Kubernetes is a infrastructure technology referenced directly in these articles, usually as a concrete tool, platform, or implementation detail rather than a broad subject category.
Why it matters
Kubernetes matters when hosting, traffic handling, deployment, automation, scaling, or security controls are part of the solution design.
In this archive
In this archive Kubernetes is treated as a specific topic worth calling out when it materially shapes the implementation, stack, or workflow being discussed. It currently appears in 11 articles and crosses 2 categories.
Nearest categories
Reference
Often appears with
KubeVirt ships Beta feature gates on by default, cross-architecture VMs, CBT backups, confidential computing, and AI/GPU placement — one control plane for VMs and pods.
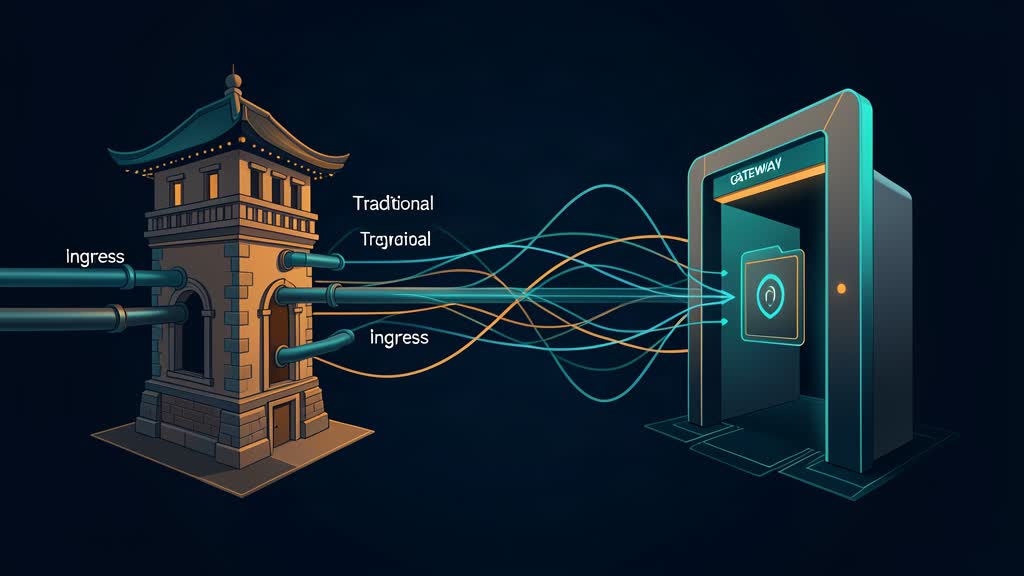
A practical 2026 guide to moving from Ingress-NGINX to Kubernetes Gateway API, with conversion steps, compatibility checks, and a safer traffic-shift plan.
A practical, measurement-first workflow for cloud cost optimization: FinOps governance, allocation, commitments, Kubernetes rightsizing, storage lifecycle policies, and egress control.
K3s is a lightweight, CNCF-certified Kubernetes distribution. See when a single-node cluster fits small teams and the availability, backup, and upgrade trade-offs.
Service mesh adoption fell from 50% to 42%, and AWS is retiring App Mesh — yet Istio and Linkerd are simpler than ever. Use this 2026 decision framework to know when to adopt a mesh and when to skip it.
A practical guide to internal developer platforms: the problem an IDP solves, platform-as-a-product principles, golden paths, self-service, tooling without lock-in, security guardrails, DX metrics, an adoption roadmap, and common pitfalls.
Cilium rewrites the service mesh rulebook by running the data plane in the Linux kernel with eBPF — no sidecar proxies per pod, lower latency, and simpler operations. How it works, where it falls short, and how it compares to Istio in 2026.
Confidential Containers advancing to CNCF incubation marks a major shift for Kubernetes security, bringing hardware-enforced data-in-use protection to mainstream cloud-native stacks.
DevOps teams using AI to write Terraform and Kubernetes config face a hard truth: only 55% of AI-generated code is secure. Here's what platform teams must do about it.
Kubernetes is still evolving, but the most useful updates in 2026 are the ones that reduce friction, simplify operations, and help teams ship safely.
The 'DevOps engineer' role is being replaced by dedicated platform engineering teams building Internal Developer Platforms. Here is what changed, why it matters, and what tools define the new landscape.